What Is DORA? Definition, Obligations, and Deadlines
Learn how DORA impacts the financial sector, key compliance requirements since January 2025, and how it differs from NIS2.
What are you looking for?

Benedikt Langer is an editor at SecurityToday. His focus areas are cloud security, zero trust and NIS2 compliance. He shapes the thematic direction and ensures editorial quality.
Learn how DORA impacts the financial sector, key compliance requirements since January 2025, and how it differs from NIS2.
Two years after the Southwestphalia IT attack, Security Today dissects: VPN without MFA, rebuilding without ransom, and five lessons for municipal IT.

CVSS alone misguides vulnerability prioritization. Exposure, exploit proximity, and asset criticality order the queue by reachable attack surface.

False-positive reduction in SOC: Detection engineering evaluates intent, telemetry, context, and escalation maturity before live deployment.
Cybersecurity budget as risk financing: five key items a CISO should fund before investing in expensive tools-and how Section 30 of Germany’s BSIG…
Private WhatsApp use in companies is a compliance risk. Which criteria a business messenger must meet and which alternative truly works.
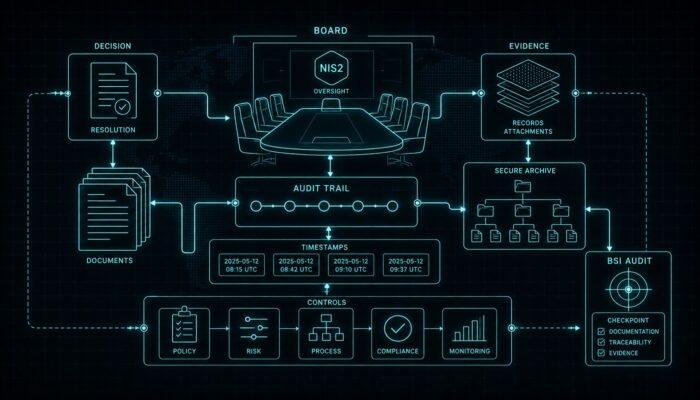
The BSI does not require a formal resolution, but verifiable implementation. Six documents that determine the evidence in the BSI audit.

How IT providers in the DACH channel share threat insights and strengthen cyber resilience through GTIA ISAO.
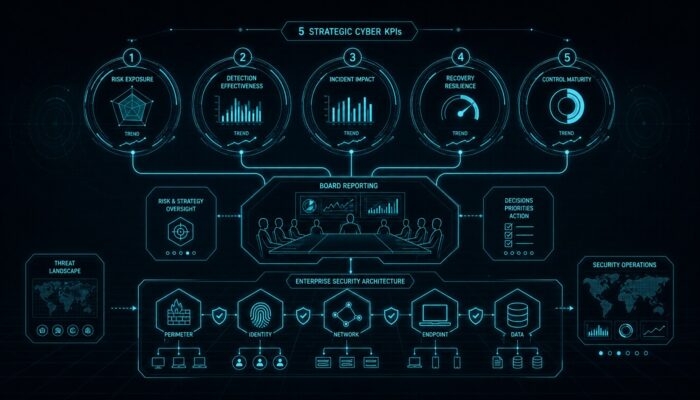
Which five key metrics a CISO should report to the supervisory board and why blocked attacks reveal little about the cyber risk situation.
Mini Shai-Hulud spreads itself via npm and PyPI: How the supply-chain worm steals tokens and what security teams need to secure now.
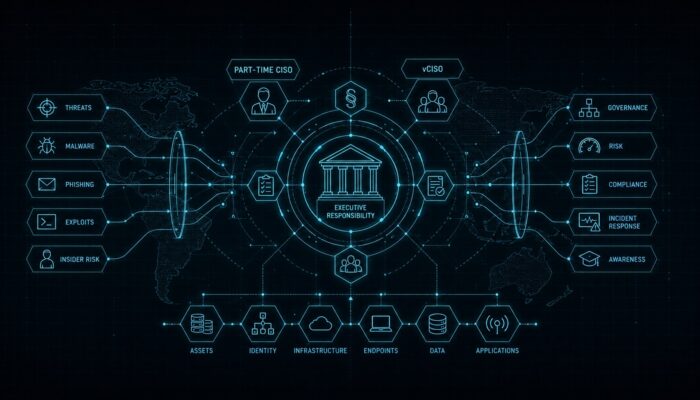
A virtual CISO takes over the security expertise in medium-sized businesses. However, certain responsibilities under Paragraph 38 of the BSIG (Federal…
The KRITIS umbrella law has been in effect since March 2026 and makes physical resilience mandatory.
ISO 27001 is often considered proof of compliance with NIS2. However, the BSI takes a different view.
A critical Oracle PeopleSoft vulnerability (CVE-2026-35273) has reportedly been exploited in ransomware attacks, according to CISA.

SearchLeak turned Microsoft 365 Copilot into a data leak via a link. What parameter injection teaches about Copilot governance and AI security.
Competitors are allowed to issue cease-and-desist letters for data protection violations.
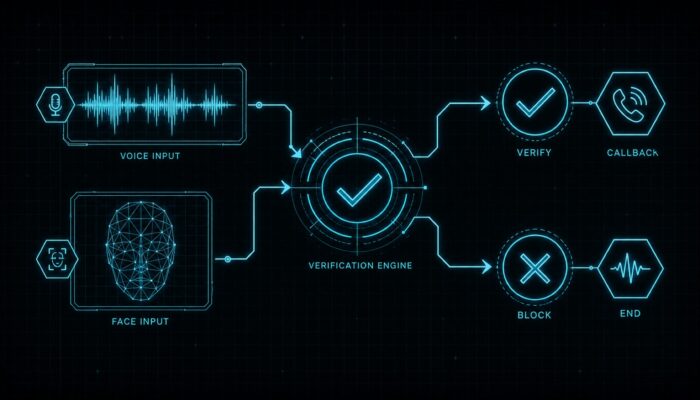
Cybersecurity against deepfakes: Just a few seconds of audio can be enough to clone a voice. What playbook protects executives from CEO fraud.
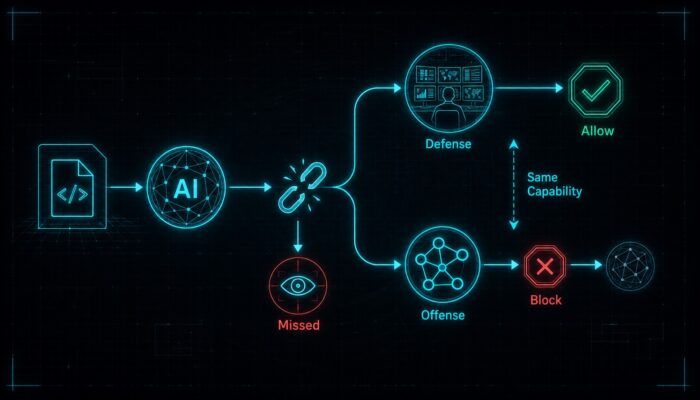
Rethinking cybersecurity: AI models find vulnerabilities that humans couldn't see. The same strength that defends and attacks - the dual-use dilemma.
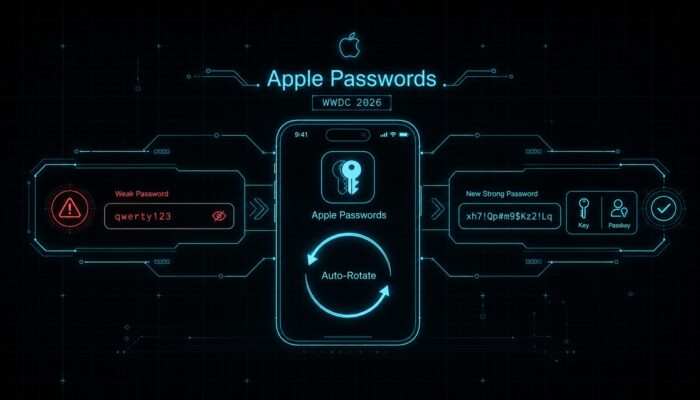
Apple's password app now proactively changes weak passwords. Why this hardens hygiene and simultaneously opens up a new attack surface.
Veeam Security Update: Two high-severity vulnerabilities affect Veeam Agent for Windows and the Linux Appliance. What admins need to patch now.

Sharing the host kernel: Why the "Copy Fail" gap breaks out of the container and which layers truly protect against kernel errors.


