The vulnerability that only AI has found
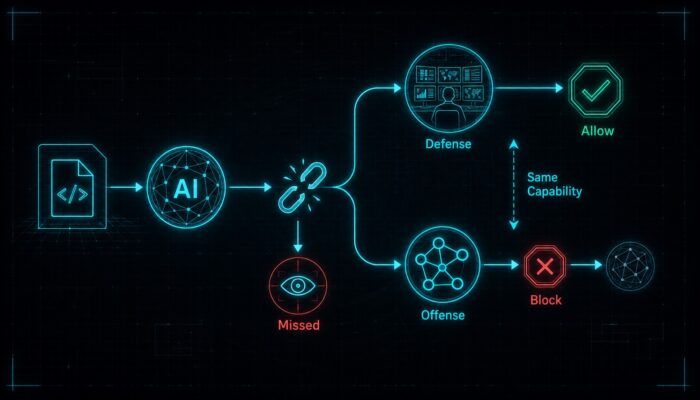
In a consortium called Project Glasswing, an AI model uncovered vulnerabilities this spring that human auditors had missed. The same model that patches these gaps could also be used to exploit them. This dual-use dilemma forces Anthropic to implement tiered access-and SOC teams to adopt a new threat model.
Key Takeaways
- The capability is real. Anthropic’s Mythos models lead in security tasks, uncovering vulnerabilities in programs like Project Glasswing that humans overlook.
- Defense and offense rely on the same strength. Whoever can reliably find vulnerabilities can also exploit them. That’s why Anthropic restricts access and reroutes high-risk requests to a weaker model.
- The threat model is evolving. SOC teams must now account for attackers who search for weaknesses at the same AI-driven speed as defenders.
Related:Patch prioritization: Why CVSS alone slows down your SOC / Security awareness: Click rates measure the wrong thing
What happened in Project Glasswing
When Anthropic unveiled its Mythos models in April, the first step wasn’t a product for the masses. The company held back its most powerful version and deployed it within a consortium: Project Glasswing. There, select firms used the model to identify and fix software vulnerabilities before attackers could discover them.
The results justified the caution. A system that detects security flaws faster and more thoroughly than an experienced team is a formidable defensive tool. Such a tool demands controlled distribution.
A model that finds vulnerabilities is equally suited for defense and attack. The search process is identical-the only difference is the objective.
Why the same capability works in both directions
Penetration testing and attacks have always relied on the same techniques, just with different intentions. In a model designed to find vulnerabilities at scale, this long-standing tension becomes a concrete governance challenge.
Anthropic’s answer is tiering. The widely available variant automatically routes higher-risk queries from cybersecurity, biology, and chemistry to a less powerful model instead of answering them itself. The strongest variant remains reserved for a small circle of defenders and infrastructure providers, sometimes in partnership with government agencies.
Mythos becomes publicly known, but its release to the general public is withheld. Launch of Project Glasswing.
The model identifies vulnerabilities within the consortium that had eluded human auditors.
The strongest variant is deployed to a tight circle of cyber-defenders; the broad variant routes risky queries onward.
What this means for SOC teams
The practical takeaway isn’t cause for alarm, but it is cause for preparation. When defenders locate gaps at AI speed, security teams must assume attackers will seek the same leverage. The window between vulnerability discovery and exploitation tends to shrink.
For your threat model, that means faster patch cycles, tighter monitoring of exposed interfaces, and the expectation that automated search will become the norm on both sides. Governance frameworks such as NIS2 already demand demonstrable responsiveness; AI-driven discovery turns that requirement into a genuine race against time.
Frequently Asked Questions
Every question is locked. A tap unlocks the answer.
What is dual-use in AI models?
Dual-use refers to a capability that can be deployed both defensively and offensively. A model that finds vulnerabilities to patch them can just as easily use that same capability to exploit them. The difference lies solely in the user’s intent.
What is Project Glasswing?
A consortium in which selected companies leverage Anthropic’s Mythos model to discover and remediate software vulnerabilities. It was the deliberately controlled path to deploying strong security capability without making it widely available.
Why does the broad model reroute risky queries?
The publicly available variant automatically passes higher-risk topics from cybersecurity, biology, and chemistry to a less powerful model. This lets full performance be offered where it’s non-critical, while throttling where abuse is a risk.
Does this mean more attacks on my company?
Not necessarily more attacks, but potentially faster ones. When automated search becomes the norm, the gap between discovery and exploitation narrows. Patch cadence and visibility of your own interfaces move to the top of the priority list.
What should an SOC team do right now?
Inventory exposed interfaces, base patch prioritization on real exploitability rather than scores alone, and expand your threat model to include AI-capable attackers. What matters most is how quickly your team responds.
More from the MBF Media Network
cloudmagazinArtificial Intelligence Is No Longer a Playground for the IT ChannelMyBusinessFutureWhen the update itself becomes an entry pointDigital ChiefsApple Builds AI as Its Moat: The Golden Gate Strategy


Further reading

WithSecure: From Antivirus Pioneer to Cloud Security Specialist
WithSecure has been F-Secure’s B2B spin-off since 1 July 2022. Its Elements platform, co-security services and European data-protection focus aim to give security teams …


