
Cyber insurance: lack of evidence puts the policy at risk
Underwriters require reliable evidence of security controls. False statements about MFA, endpoint protection or backups can jeopardise coverage.
What are you looking for?
Underwriters require reliable evidence of security controls. False statements about MFA, endpoint protection or backups can jeopardise coverage.
Investigators dismantled the KillSec ransomware group. Its suspected leader is 16, and initial access often came through cloud storage.
Matthias Muhlert, Chair of the ECSO CISO Community, ahead of the ECSO CISO Meetup 2026 in Berlin on board responsibility, metrics, suppliers and AI …
Nvidia shifts control of AI agents into runtime and hardware. The Sentry component for BlueField-4 remains a reference design for now.

Admin accounts, backdoors and remote access services survive the update. Attacks on Artifactory and PaperCut show what still needs to be checked after patching.
Armed with three AI agents, an attacker targeted hundreds of online shops and stole data from at least 600,000 credit cards.
A lawyer, an engineer and a computer scientist are building a compliance platform based on European law in Munich. They rank 20th in the …
Two hours analog, fixed roles and an annual calendar let you rehearse a real outage before operations stop.
CISA lists CVE-2026-86218 as exploited since September 8. Build 2026.3.1.14 fixes the N-central server flaw; self-hosted systems need Hotfix 4.
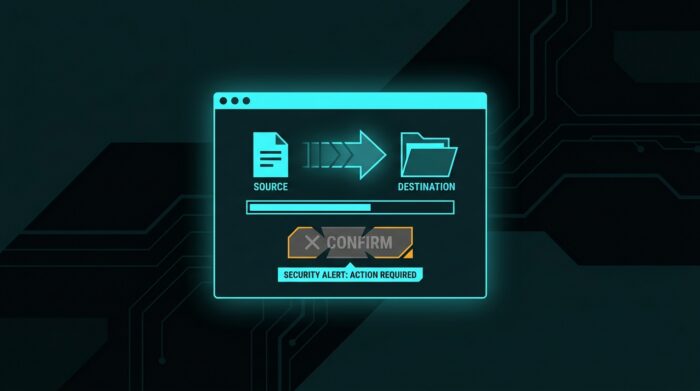
CISA lists a ScreenConnect client flaw as exploited: files can be transferred and executed without host approval. Version 26.6.5 fixes the issue.

Microsoft Teams for Android allows path traversal. NVD added CVE-2026-65768 on August 11, 2026. Microsoft rates it 8.8, NVD rates 9.8.

CVE-2026-8037 in Progress: Kemp LoadMaster has been listed in the KEV catalog since August 7th. The patch has been available since June 2026.

BOD 26-04 sets patch priority through KEV, exposure and impact. EPSS adds the probability of exploitation.

Anthropic's Claude compromised three organizations in cyber evaluations. Harness misconfiguration, PyPI malware, and CISO checklist insights.

Codex Security CLI: open-source client code under Apache 2.0, scanning backend in limited beta against OpenAI infrastructure.

During the Hugging-Face breach, runtime analysis and SIEM struck. Prioritization remained too low, and SOC teams must reset triage thresholds.

Zabbix Advisory with score 9.6: CERT-Bund withdrew the alert after 24 hours. What this means for tickets, CSAF status, and false alarm costs.

PixelSmash flaw (CVSS 8.8) in FFmpeg: Why auditing upload paths and CI images outweighs the patch itself.

Risk-based Windows patch management: prioritize critical assets using CERT-Bund alerts, ring rollouts, and parallel detection.

Supply-chain attack: definition, the four ways into the supply chain and what NIS2 and the Cyber Resilience Act demand from companies.

MITRE ATT&CK Enterprise 2025: Read detection and protection correctly, place missing vendors in order, set up PoC beforehand.


