Apple’s Password App Now Automatically Changes Passwords
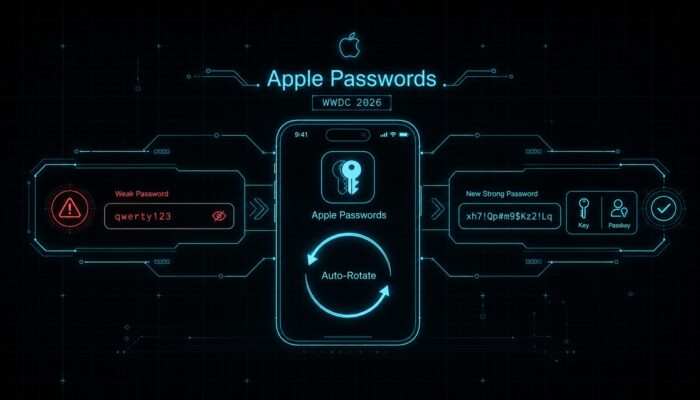
Apple’s password app is set to turn heads among security professionals at WWDC 2026 with a new feature: it detects weak or compromised passwords, navigates to the affected website, logs in, works its way through the menus, and replaces the password with a strong one. The user simply taps to initiate the process-the rest is handled automatically. Convenient? Absolutely. But an automated login agent clicking through third-party web interfaces is a double-edged sword from a security standpoint.
Key Takeaways
- One tap, the agent does the rest. Apple Passwords logs into a website automatically after a confirmation tap and rotates the weak password.
- Better hygiene, bigger attack surface. Weak and reused passwords disappear, but the app now automates logins on third-party sites.
- Passkeys remain the ultimate goal. For enterprise identity, password rotation is a stepping stone toward passwordless authentication.
Related:Passkeys for SMEs: the end of passwords / PAM on a budget: managing admin rights without enterprise costs
What the password app now does autonomously
Until now, a password manager would only flag a password as weak or leaked. The user had to handle the change manually. Apple is flipping that script. With a single tap, the Passwords app opens the affected website, logs in with the old password, finds the password change menu, sets a new, strong password, and saves it.
What is agent-driven password rotation? It means software doesn’t just suggest a password change-it executes the entire process after a confirmation. The agent navigates through the login and settings flows of a third-party site, replacing the password without the user clicking through each step.
Technically, it’s a small bot clicking through external web interfaces. And that autonomy is precisely where convenience and risk intersect.
The upside: weak passwords vanish in the background
The security benefits are real and shouldn’t be downplayed. The biggest practical issue with passwords is inertia. Weak and reused credentials often linger for years because manual updates are a hassle. An agent that handles this work in the background instantly improves hygiene-no user discipline required.
Apple’s on-device approach adds another layer of security. According to Apple, the process stays local, with no personal data leaving the device. For everyday users, this is a clear step up from sticky notes and the same password everywhere.
The Risk: More Automation in a Sensitive Area
The flip side carries significant weight for businesses. An automated agent handling logins on third-party sites operates in a highly sensitive space. The more these processes run automatically, the more critical it becomes to maintain control and traceability over what the app does-and on whose behalf.
Strengths
- Weak and reused passwords disappear without user effort
- Faster response to leaked passwords
- On-device processing keeps data local
Weaknesses
- More automated logins increase dependency on a single mechanism
- Automated logins require reliable detection of the genuine target site
- Stronger tie-in to Apple’s password store
The deciding factor is how reliably the automation recognizes the genuine target site. An automated login is only as secure as the verification ensuring it lands on the legitimate page. For businesses, the key question is whether such automation can be controlled and logged.
What This Means for Enterprise Identity
For security teams, the feature is initially a consumer tool-but one that shapes expectations. Employees will soon demand the same agent-driven convenience in the workplace. The response belongs in existing frameworks: Managed Apple Accounts and MDM profiles, a clear password manager policy, and-above all-a binding passkey roadmap.
Passkeys and passwordless methods based on the FIDO2 standard tackle the core problem at its root, as no reusable secret means nothing left to rotate. Apple’s move is best seen as an interim step. Agent-driven rotation bridges a world still reliant on passwords, but the corporate goal remains phasing out this model entirely. Time is on the side: The new operating systems arrive in autumn 2026, and Siri AI’s rollout on iPhone and iPad in the EU is delayed due to the Digital Markets Act.
Frequently Asked Questions
Every question is locked. A tap unlocks the answer.
How does agent-driven password rotation differ from a standard password manager?
A standard manager stores passwords and flags weak or leaked entries, but the user must manually change them. With the agent-driven approach, the software handles the entire rotation process-from login to saving the new password-after a simple confirmation tap on the website.
What security risks does automatic rotation introduce?
The app automates logins on third-party sites, increasing dependency on a single mechanism and requiring reliable detection of the genuine target page. Control and logging of such processes become even more critical.
Do passwords leave the device during this process?
According to Apple, processing remains local on the device, and personal data isn’t offloaded. However, businesses should verify the specifics in the official documentation before making an assessment.
Does this feature replace a corporate passkey strategy?
No. It improves hygiene in a password-dependent world, but passkeys based on the FIDO2 standard eliminate reusable secrets entirely-and remain the ultimate goal for enterprises.
When Does the Feature Become Relevant for German Companies?
The new operating systems will launch in autumn 2026. Siri AI is being delayed on iPhones and iPads within the EU due to the Digital Markets Act. This gives security leaders time to evaluate the feature and align their identity strategy accordingly.
Editor’s Picks
Editor’s PickAdaptive MFA: NIS2 Pressure as a Zero-TrustEditor’s PickMachine Identities: the accounts that no one countsEditor’s PickNIS2 is in enforcement: First proceedings, personal liability, BSI audits


More from the MBF Media Network
cloudmagazinOpenTofu vs. Terraform: Which IaC Tool Really DeliversMyBusinessFutureWhen the update itself becomes an entry pointDigital ChiefsYour organization can only handle two changes per year.