Ivanti Connect Secure Back on CISA KEV: 3rd Incident in 18 Months
7 Min. Reading Time · Threat Briefing
The CISA has added another Ivanti Connect Secure vulnerability to its Known Exploited Vulnerabilities catalog this week. This marks the third major incident involving the VPN gateway manufacturer in 18 months. Mandiant is observing active exploitation by state-sponsored groups in at least three DACH KRITIS sectors. Meanwhile, Eclypsium has released technical indicators suggesting in-memory persistence. The M-Trends 2026 report ranks VPN appliances as the number one initial access vector for the second year in a row, ahead of exposed edge services and phishing. For CISOs, this isn’t just a patching issue; it’s a strategic question: How long will Ivanti remain in the critical path, and if so, under what conditions?
Key Takeaways
- Third Ivanti incident in 18 months: The cumulative trust issue with the manufacturer is escalating. Structural problems in the secure development lifecycle are no longer isolated incidents.
- VPN appliances remain top initial access vector: Mandiant’s M-Trends 2026 report documents this in 38% of corporate incidents. Edge devices are the most exposed element of corporate topology in 2026.
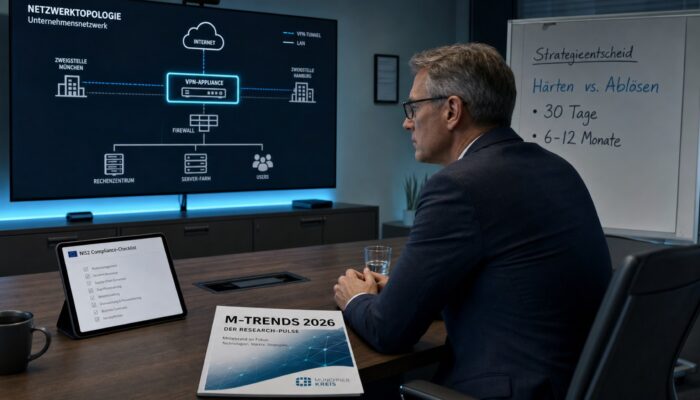
- Hardening or replacement: CISOs face a decision in 2026 that is no longer just tactical. Rapid hardening within 30 days is possible, but replacement takes six to twelve months and requires board approval.
RelatedeBPF Monitoring in Kubernetes / Detection Engineering Without Vendor Lock
What’s Happened
The new CVE affects Ivanti Connect Secure and Ivanti Policy Secure in several actively used versions. CISA added the vulnerability to the KEV within 48 hours of its disclosure, with a federal deadline for affected US agencies within two weeks. In the DACH region, the deadline is not binding, but the KEV listing serves as an unofficial trigger for every serious CISO standard.
Mandiant reports in its flash update that the vulnerability is being actively exploited, with patterns indicating an already established state-sponsored cluster activity. Initial indicators were observed in DACH energy and telecommunications networks. Eclypsium has published technical details on an in-memory persistence mechanism that bypasses classic patching routines: the patch closes the initial gap but does not remove the backdoor anchored in RAM. Those who only patch and do not reboot and conduct forensic analysis have not eliminated the risk.
Ivanti provided a hotfix package within 24 hours. In the first 72 hours after release, about 60% of exposed devices were patched based on DACH NOC telemetry, which is faster than in the two incidents in Q4 2024 and Q2 2025. The operational reflex is in place, but it is no longer sufficient to address the trust issue in 2026.
Escalation Situation 2026
According to Mandiant’s M-Trends 2026, 38% of all corporate incidents start with a VPN or edge appliance. This is the third Ivanti Connect Secure incident in 18 months. CISA KEV listing within 48 hours. At least three DACH KRITIS sectors are actively affected. Patching alone is not enough: in-memory persistence requires reboot and forensic examination.
What CISOs Need to Decide Now
Three decision areas cannot be delegated to the operations layer in 2026.
Immediate Hardening within 30 Days. Patch plus reboot plus indicator sweep is the minimum. If you want to keep Ivanti appliances in 2026, you should also enforce multi-factor authentication at the VPN gateway, limit session limits, activate geographical login filters, and sharpen monitoring for SAML token anomalies. These are 30-day measures that are feasible in a serious SOC.
Medium-term Architecture Decision within Six Months. Will Ivanti remain in the key path, or will the organization migrate to a Zero Trust Network Access architecture? ZTNA solutions like Zscaler Private Access, Cloudflare Access, or Netskope Private Access reduce the attack surface because there is no directly exposed VPN appliance. The migration takes six to twelve months and requires board mandate plus a budget of between 600,000 and 2.4 million euros for medium-sized DACH setups.
Vendor Diversification as a Strategy. Even if you keep Ivanti, you should not connect all locations through one manufacturer in the medium term. Dual-vendor strategies with two VPN or ZTNA providers on critical locations reduce the single-vendor lock risk, which became a crisis again from 2024 to 2026.
Pros and Cons of the Three Paths
Pro Patch + Hardening
- Fastest path, 30 days realistic
- No architecture change needed
- Existing team skills can be utilized
- Justifiable if the incident were a one-time event
Contra Patch + Hardening
- Structural vendor trust risk remains
- Next incident is statistically due
- Reputation with authorities is compromised
- Costs accumulate over incidents
Pro ZTNA Migration
- Attack surface significantly reduced
- Zero Trust standard during audits
- Cloud-native integration with IdP
- Reduces edge appliance complexity
Contra ZTNA Migration
- Six to twelve months migration time
- Budget impact six-figure to seven-figure
- Board mandate required
- Learning curve for team and users
Pro Dual-Vendor
- Risk distribution across two manufacturers
- Negotiation leverage during procurement
- Faster switch in case of vendor crisis
- Pragmatic compromise
Contra Dual-Vendor
- Double operational complexity
- Two update cycles, two audit trails
- Higher license costs in total
- Growing skill requirements
The 30-60-180 Day Plan
Operational Sequence after KEV Listing
Day 1 to 7. Deploy patches, reboot all appliances, perform Indicator-of-Compromise sweep against Eclypsium and Mandiant indicators, invalidate affected sessions, rotate all active SAML tokens.
Day 8 to 30. Conduct in-depth forensic examination of appliances for in-memory persistence, enforce MFA for VPN login, activate geo-filtering, restrict session limits, refine SOC detections for SAML token anomalies.
Day 31 to 90. Conduct architecture review with executive board: prepare for ZTNA migration or set up dual-vendor plan, renegotiate procurement contracts with security SLA clauses, review NIS2 reporting requirements for affected subsidiaries in DACH region.
Day 91 to 180. Launch ZTNA pilot in two business areas, prepare dual-vendor setup for critical locations, incorporate lessons learned into group standards, commission external audit validation.
Frequently Asked Questions
Every question is locked. A tap unlocks the answer.
How severe is the third Ivanti incident compared to the previous ones?
Comparable in impact, more severe in terms of trust. The third incident in 18 months shifts the focus from a single incident to a structural supplier issue. Regulatory bodies, insurers, and cyber insurance carriers will increasingly request a concrete action plan in 2026, rather than just a patch confirmation.
Which indicators should SOC teams implement now?
Mandiant and Eclypsium have published hash indicators, IP ranges, and behavioral indicators. SOC teams should set up YARA rules against in-memory persistence signatures, Sigma rules for SAML token reuse anomalies, and EDR detections for anomalous outbound connections from the VPN appliance. Falco or Tetragon with eBPF telemetry provides the most reliable visibility.
Are NIS2-compliant organizations required to report the KEV listing?
Not the listing itself, but every confirmed incident. If an organization detects hints of successful exploitation in its telemetry, it must report within the NIS2 deadlines: 24 hours for early warning and 72 hours for the incident report. A mere KEV listing without own indicators is not reportable.
Is immediate ZTNA migration worthwhile?
If the organization is already planning to reassess its edge architecture within the next 18 months, yes. ZTNA not only addresses the Ivanti issue but also reduces other VPN risks and provides a better audit position for NIS2 and cyber insurance. However, rushing into ZTNA without strategic planning can introduce new complexity.
What is the most common mistake after a KEV listing?
Patch and file closure. In-memory persistence is often overlooked because the vulnerability is considered closed. A serious response includes patching, rebooting, forensic examination, and at least 90-day monitoring. Reducing this to Day 1 does not eliminate the risk but merely removes it from reporting.
Editor’s Reading Tips
- eBPF Monitoring in Kubernetes: Detecting Invisible Runtime Threats
- Detection Engineering without Vendor Lock: Wazuh Stack 2026
- NIS2 Audit: Where the Vendor List Breaks Down in Two Hours
More from the MBF Media Network
cloudmagazinAI devours electricity, the cloud gets the billMyBusinessFutureProductivity Over Austerity: How SMEs Will Benefit in 2026Digital ChiefsPost-Quantum Cryptography: The Countdown for Corporate IT Is Running