The concentration risk no supplier audit sees
Why single audits miss concentration risk and how a board steers concentration and fourth-party risk.
What are you looking for?

Tobias Massow is Managing Director of Evernine Media GmbH and publisher of SecurityToday. He oversees the strategic direction of the magazine and the entire MBF Media network.
Why single audits miss concentration risk and how a board steers concentration and fourth-party risk.
From September 11, 2026, a new obligation applies that many companies still underestimate. Anyone selling connected products in the EU must report actively exploited …
The BSI will launch the first NIS2 audits for KRITIS energy suppliers in summer 2026. What OT Zero Trust really needs to deliver - …
DORA and NIS2 are interconnected, with audit paths running in parallel. Three realities that cause banks to stumble during dual implementation.
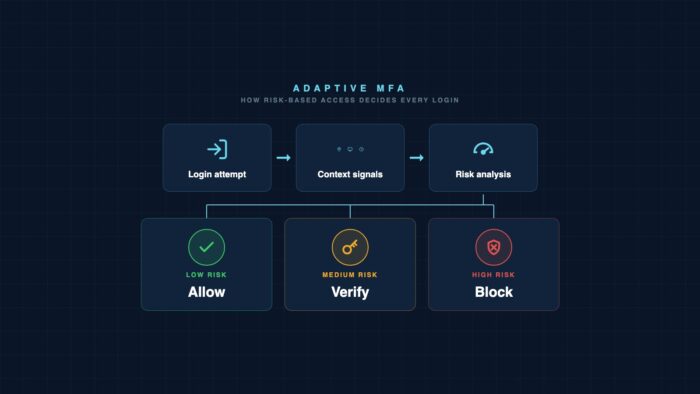
Adaptive MFA is usually enabled but not set up: How risk-based authentication truly protects beyond factory settings.
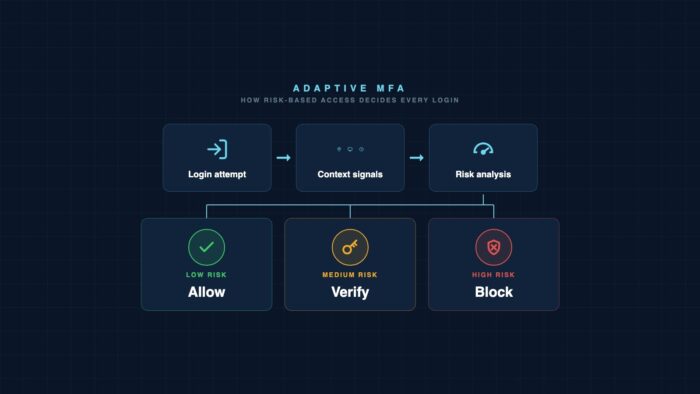
Adaptive MFA is typically enabled by default, but not configured: How risk-based authentication beyond factory settings truly protects.
NIS2 check for SMEs: five technical gaps that stand out in an audit and how to close them before the first review.
CISA has added a new Ivanti Connect Secure vulnerability to the KEV. Mandiant reports active exploitation in critical infrastructure networks.
AI phishing bypasses classic email filters like Gmail, SpamAssassin, and Proofpoint. What CISOs need to change in detection architecture in 2026.
A critical vulnerability in the most widely used hosting interface in the German Mittelstand gives attackers full access without login. The BSI has responded, …
Trellix, Okta, LastPass - three security vendors, three source code breaches, one pattern. Attackers deliberately compromise security vendors to learn about vulnerabilities in their …
CVE-2026-3854 (CVSS 8.7): GitHub Enterprise RCE via git push. 88% of self-hosted instances unpatched. Patches available since March 10th.
Bitwarden-CLI 04/22/2026: The GitHub Action checkmarx/ast-github-action is the lever. Check CI runners and action hashes for DACH-DevSecOps now.
April 2026: Wave of Healthcare Breaches. Anonymous DACH Incident Report with 500k patient data, 96h reconstruction, NIS2/DSGVO obligations.
PaperCut NG/MF has been back in the CISA-KEV since April 20, 2026. CVE-2023-27351 is being actively exploited. 72-hour inventory sweep and hardening measures for …
RedLine, Lumma, Raccoon: Infostealer malware steals session cookies and bypasses MFA. What truly works in 2026.

Starting June 2026, Microsoft's 2011 Secure Boot certificates will expire. IT teams have two months to complete inventory and deployment.

From 09/11/2026, the CRA reporting obligation applies: 24-hour early warning, 72-hour full report, 14-day final report. What security teams must now establish.
Anthropic has built an AI model that finds vulnerabilities faster than most security teams. Claude Mythos discovered a 27-year-old bug in OpenBSD and several …
Gmail rejects emails without DMARC. How to set up SPF, DKIM, and DMARC correctly in 5 days.
NIST has finalized three post-quantum standards. BSI deadline 2030/2032. Why PQC migration must start now.


