Backup against ransomware: 3-2-1-1-0 instead of 3-2-1
Most backup concepts are built for disk failure, not an active attacker. Modern ransomware targets the backup first – deleting or encrypting it to strip the victim of their strongest leverage against extortion. A backup that holds up under real pressure doesn’t just follow the old three-copy rule; it follows a harder version. What matters is a passed restore test, not the documentation in the concept paper.
Key Takeaways
- Ransomware targets the backup. According to Sophos, attackers attempt to compromise backups in 94 percent of cases. Organizations that only protect against hardware failure are planning around the wrong threat model.
- 3-2-1-1-0 closes the gap the old rule leaves open. An immutable copy and an offline copy put the backup out of an attacker’s reach. The zero stands for zero errors in the recovery test.
- Without a restore test, there is no proof. A backup that has never been restored is not a reliable recovery path. Only regular restore tests reveal whether data, permissions, and dependencies actually work when it counts.
Related:The Edge Device as a Ransomware Entry Point / NIS2 Is Now Being Enforced
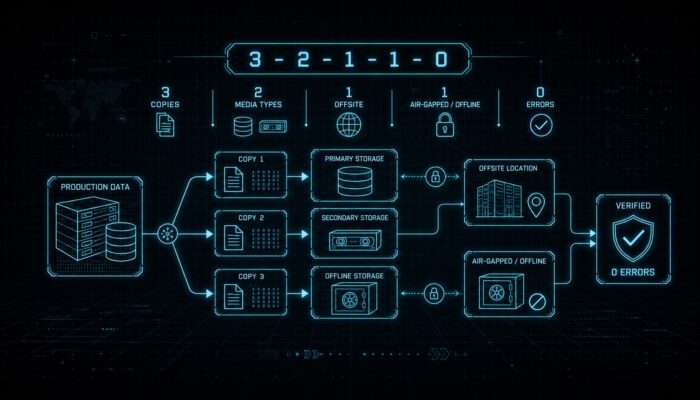
What is the 3-2-1-1-0 rule? This extended backup strategy follows a fixed pattern. Three copies of the data are stored on two different media types, one of them at a separate location. On top of that comes an immutable or offline copy, and the requirement that recovery must be tested with zero errors. It hardens the classic 3-2-1 rule specifically against ransomware.
Why ransomware goes after backups first
A well-planned ransomware attack doesn’t encrypt immediately. It moves through the network first, locates backup systems, and disables them before touching production data. The logic is straightforward: a victim with an intact backup can restore. Without a reliable copy, the options narrow to payment, full rebuild, or data loss. The backup itself becomes the primary target.
Incident data consistently reflects the same pattern. In the vast majority of cases, attackers actively attempt to compromise backups – and in more than half of those cases, they succeed. When the backup fails, recovery costs climb sharply because the fast path back no longer exists.
That changes the requirement entirely. Having a backup is not enough. It must survive an attacker who is actively hunting for it. A backup system reachable with the same credentials as the rest of the network remains part of the compromisable infrastructure.
What 3-2-1-1-0 demands beyond the original rule
The classic 3-2-1 rule dates from an era when data loss was primarily a technical event: a failed drive, a fire, an accidental deletion. Against those scenarios it still holds up. Against an attacker who is actively working through your infrastructure, it has a gap. The two additional digits close exactly that.
| Digit | Meaning | Protects against |
|---|---|---|
| 3 copies | Original plus two backups | isolated data loss |
| 2 media | two different storage types | media failure |
| 1 offsite | one copy at a separate location | site-level damage |
| 1 immutable or offline | a copy that cannot be deleted or is fully disconnected | ransomware access |
| 0 errors | verified restore | silent failure when it counts |
The first three digits remain the familiar rule. The fourth digit and the zero harden it against ransomware. At least one backup sits beyond the attacker’s reach. Recovery is tested, not merely documented.
What immutability and air-gapping deliver when it matters
Behind the fourth digit lie two concepts that are often used interchangeably but do not mean the same thing. Immutability means the backup cannot be modified or deleted for a defined retention period – not even by an administrator with stolen credentials. Technically, this relies on mechanisms such as Object Lock or write-once storage that accepts data exactly once.
An air gap means separation. The copy sits logically or physically outside every network an attacker can reach. Only when both properties are combined do you get a backup that reliably survives a determined attack. An immutable copy on a reachable system can be circumvented if the attacker is able to manipulate the retention rules. A disconnected copy without write protection can be overwritten the next time it is connected. The combination is where a backup becomes truly secure.
The Test Nobody Runs
The zero in the rule is the most uncomfortable position, because it demands work. Writing a backup is routine; restoring one is not. That is precisely why the restore test remains theoretical in many organizations – until an incident forces the issue. Then it turns out the backup was incomplete, a key is missing, recovery takes days instead of hours. These surprises belong in the test, not in the incident.
What fails
- Backups accessible with the same admin credentials as the production network
- Immutability assumed but never verified against tampering
- Restore practiced only on paper, never under real conditions
- Recovery time unknown until an incident measures it
What holds
- One immutable and one separate copy stored outside the domain
- Dedicated credentials for the backup system, isolated from day-to-day operations
- Regular restore tests with measured recovery times
- An isolated recovery environment ready for the real emergency
The difference between the two columns requires no additional license. It requires discipline. A backup is not a purchase you check off a list – it is a process that must be proven. Anyone who takes the fourth position seriously and tests the zero regularly will have, when it matters, the one lever that renders an attack useless.
Frequently Asked Questions
Every question is locked. A tap unlocks the answer.
What exactly does the extended backup rule mean?
Three copies of the data on two different media, one of them at a separate location. Add to that an immutable or offline copy, and the requirement that recovery has been tested with zero errors. The last two elements specifically harden the classic 3-2-1 rule against ransomware that targets backups directly.
Why is the old 3-2-1 rule no longer enough?
It protects against technical data loss such as hardware failure, fire, or accidental deletion – but not against an attacker actively probing your infrastructure. If all copies are online and reachable with the same credentials, ransomware can encrypt them too. Only an immutable or air-gapped copy closes that gap.
What is the difference between immutability and an air gap?
Immutability means a backup cannot be modified or deleted for a defined period – even with admin rights. An air gap means physical or logical separation from any reachable network. Only when both properties are combined do you get a copy that reliably survives a serious attack. Either alone can be circumvented.
How often should you run a restore test?
Regularly – and for truly critical systems, at least quarterly. What matters is not just testing whether individual files can be read back, but verifying the complete restoration of a system including the measured time it takes. Only then does “the backup works” stop being an assumption and become a concrete, defensible number.
What is an isolated recovery environment?
A segregated area where systems can be restored from backup and verified without touching a production network that may still be compromised. This ensures the recovery is clean and does not reintroduce the same malicious code that triggered the incident in the first place.
Editor’s Picks
Editor’s PickCyber Liability in Administration: Three Levels, No PlanEditor’s PickLinux Kernel Vulnerabilities: BSI Warns of Root EscalationEditor’s Pick14 Malicious npm Packages in Four Hours: Why Static Third-Party Checks Are No Longer Enough


More from the MBF Media Network
cloudmagazinPlatform Engineering is no longer just a DevEx projectDigital ChiefsManaged Security Services: CISO Does Not Bear Sole LiabilityMyBusinessFutureStanford AI Index 2026: Inaccuracy overtakes cybersecurity as top risk – what SMEs must measure