
Cisco Catalyst SD-WAN Manager: Three CVEs, CISA Deadline April 23
CISA has added three Cisco SD-WAN Manager CVEs to the KEV. Deadline: April 23. Why the attack chain hits DACH networks.
What are you looking for?

Benedikt Langer is an editor at SecurityToday. His focus areas are cloud security, zero trust and NIS2 compliance. He shapes the thematic direction and ensures editorial quality.
CISA has added three Cisco SD-WAN Manager CVEs to the KEV. Deadline: April 23. Why the attack chain hits DACH networks.
Shadowserver identifies 6,364 vulnerable Apache ActiveMQ instances on 19 April 2026. CISA lists the CVE as actively exploited. What DACH security teams need to …
BSI published advisories on F5 BIG-IP, Citrix NetScaler, and Trivy in March/April 2026. What operators of critical infrastructure must patch and report this week.
Which security conferences in 2026 deliver real value and where the ROI turns—RSAC, it-sa, Black Hat Europe, DEF CON under sober editorial review.

Deepfake CEO fraud is real: USD 25M in the Arup case. How companies can protect their payment processes.

The open-source agent OpenClaw has become the primary distribution channel for Chinese AI services globally. Over 42,900 exposed instances, prompt injection risks, and data …
North Korean hackers compromised two versions of the npm package Axios and injected a cross-platform remote access trojan. With over 100 million weekly downloads, …
Most Kubernetes breaches result from misconfigurations. 8 concrete measures to harden your cluster in 5 days.

A missing exclusion rule in the build pipeline exposed Anthropic’s full production code on March 31, 2026. 512,000 lines of TypeScript, packaged into a …
For 36 days, attackers gained unauthenticated root access to Cisco Secure Firewall Management Center - before Cisco released a patch. The Interlock ransomware group …

80 percent of all data breaches begin with stolen or compromised credentials. 40 percent of these involve privileged accounts: domain admins, service accounts, database …

Software stocks plummet as AI agents are set to automate entire business processes. Yet while executives debate cost savings, a security issue is emerging …

On March 19, 2026, the popular vulnerability scanner Trivy itself became an attack vector. 75 out of 76 version tags in the GitHub repository …

BGH 2025: Competitors may issue GDPR warnings. 100 euros compensation per affected person. Most common pitfalls and how companies can protect themselves.

178.6 billion euros in cyber damages, 309,000 new malware variants daily, 22 APT groups active. Top 10 cyber risks with BSI, Bitkom, and ENISA …
119 ransomware groups target industrial organizations. 81% lack IT/OT segmentation. What manufacturers must do now.
454,648 new malicious packages identified in open-source registries in 2025 alone - 75 percent more than the previous year. And in March 2026, the …

Cooling failures, not cyberattacks, cause most unplanned data center outages. NEXAIRA.Systems by ebm-papst adds anomaly detection and predictive maintenance.
Zero Trust made a promise: Trust no one, verify everything, minimize the blast radius. But attackers have adapted. They don’t break in anymore - …

Deutsche Bahn alone manages 500,000 software bills of materials. What sounds like bureaucracy will become mandatory for every manufacturer of digital products in the …
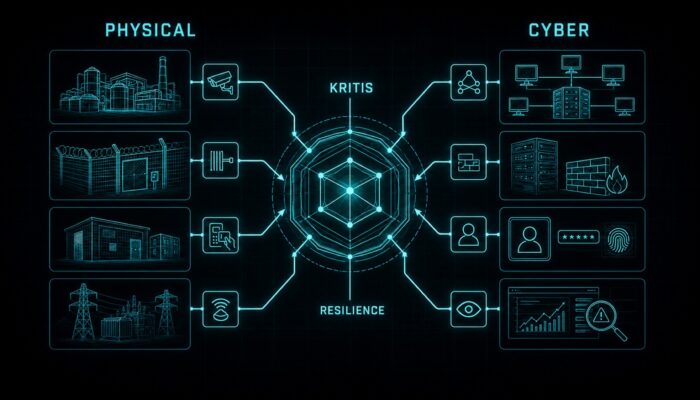
KRITIS protection becomes physical: The umbrella law obliges around 1,300 operators to be resilient against all hazards.


